Configuring SAML Authentication
SAML, or Security Assertion Markup Language, is an XML-based framework for exchanging authentication and authorization data between parties.
It enables Single Sign-On (SSO) across different domains or systems by allowing an entity, known as the identity provider, to authenticate a user and generate security assertions. These assertions are then shared with service providers to grant access.
SAML facilitates secure communication and seamless resource access without requiring users to log in repeatedly. Orchestra allows configuration of the login process according to your identity provider, using the SAML login flow to access the Orchestra Monitor.
Configuration of SAML Authentication
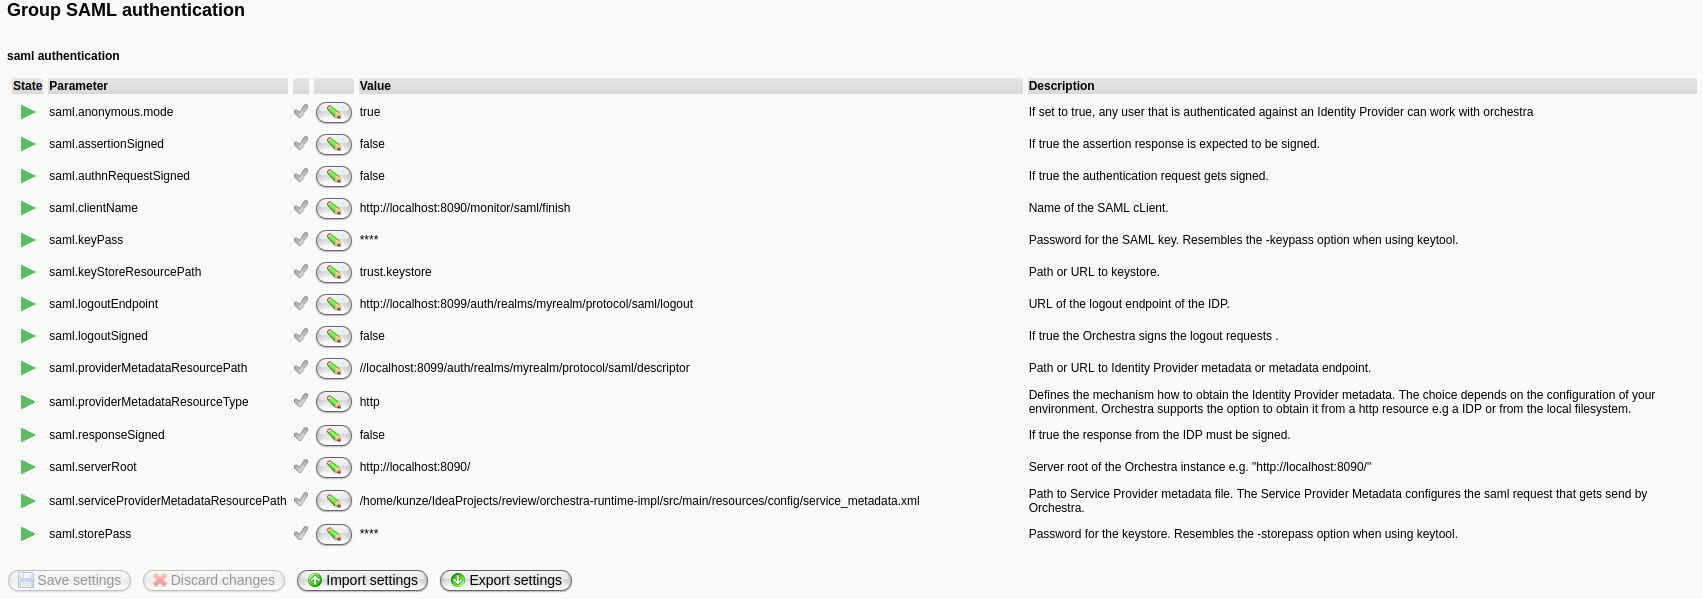
| Parameter | Description |
|---|---|
saml.anonymous.mode | If set to true, the Monitor redirects to the login site of the identity provider. |
saml.assertionSigned | If set to true, the assertion returned from the identity provider is expected to be signed. |
saml.authnRequestSigned | If set to true, the authentication request will be signed. |
saml.clientName | Name of the SAML client. |
saml.keyPass | Password for the key pair used for SAML. |
saml.keyStoreResourcePath | Path or URL to the keystore that holds the SAML key. If no keystore exists at this path, a new one will be created. |
saml.logoutEndpoint | The logout endpoint of the identity provider. |
saml.logoutSigned | If true, Orchestra signs the logout requests. |
saml.providerMetadataResourcePath | Path or URL to the identity provider's metadata file or endpoint. |
saml.providerMetadataResourceType | Defines the mechanism for obtaining the Identity Provider metadata, which can be acquired from an HTTP resource (e.g., an IDP) or the local filesystem. |
saml.responseSigned | Orchestra expects the SAML response to be signed. |
saml.serverRoot | The server root of the Orchestra instance, e.g., "http://localhost:8090/". The protocol, host, and port are required. |
saml.serviceProviderMetadataResourcePath | Orchestra automatically generates the service provider metadata. This parameter defines the location where Orchestra saves the metadata file (filename must be specified, e.g., service_metadata.xml). |
saml.storePass | Password for the keystore defined in saml.keyStoreResourcePath. If the keystore doesn't exist, it will be generated automatically. |
Configuration of the saml_security_groups.xml
The saml_security_groups.xml file is used to define your Orchestra role mapping.
Refer to Configuring SAML Role Mapping for detailed documentation.